

SHIFT Launches “THREAT-AQ,” a New Security Operations Service Combining Threat Intelligence and AI Analytics
SHIFT Launches “THREAT-AQ,” a New Security Operations Service Combining Threat Intelligence and AI Analytics
Delivering continuous high-precision risk insights and recommended countermeasures by leveraging threat intelligence and proprietary AI to analyze external security risks—including vulnerabilities, credential leaks, and impersonation—backed by expert analyst evaluations.
SHIFT Inc. (“SHIFT,” headquartered in Minato-ku, Tokyo, Japan; Masaru Tange, CEO and Representative Director), a provider of business transformation services rooted in quality, today announced the launch of “THREAT-AQ,” a new security operations service that combines threat intelligence and AI-driven analytics, starting Thursday, October 15, 2026.
THREAT-AQ visualizes external security risks exposed on the internet—such as vulnerabilities in public-facing IT assets, misconfigurations, confidential data leaks, and impersonation—based on client domain information. Detected risks are rapidly analyzed using threat intelligence and SHIFT’s proprietary AI technology, then evaluated by dedicated security analysts to clearly prioritize response efforts.
By combining AI-powered rapid threat analysis with specialized expertise built over nearly four years of internal group Attack Surface Management (ASM) operations, THREAT-AQ delivers continuous, highly accurate risk intelligence and actionable recommendations to help organizations proactively prevent cyberattacks.
Service Page: https://contents.shiftinc.jp/threat-aq/
[Background of Brand Launch]
Driven by the growing sophistication and speed of cyberattacks following the rapid adoption of generative AI, incidents such as large-scale unauthorized access and personal data leaks targeting Japanese organizations have surged in recent years, becoming particularly pronounced since late September 2026.
In October 2026, JPCERT/CC issued an alert (*1) highlighting a sharp rise in attacks exploiting cybersecurity vulnerabilities in externally observable IT assets (attack surfaces) in connection with recent major data breaches. Furthermore, in the same month, Japan’s National Institute of Information and Communications Technology (NICT) reported (*2) that “App-to-Backend (A2B) attacks”—where backend servers are compromised via public application and API analysis—are behind the recent wave of data leaks. As traditional, periodic methods like standard vulnerability assessments prove insufficient, managing risks on externally exposed IT assets through Attack Surface Management (ASM) has become an urgent priority.
The SHIFT Group launched its security business in 2016 and, as part of its security enhancement initiatives, began implementing internal ASM operations in 2022. By integrating this proven ASM operational expertise with its AI capabilities, SHIFT is launching “THREAT-AQ” to provide a new security operations service powered by threat intelligence and AI analytics.
(*1) JPCERT/CC: “Alert Regarding Recent Successive Unauthorized Access Incidents in Domestic Organizations” (Published October 2026) https://www.jpcert.or.jp/at/2026/at260030.html
(*2) National Institute of Information and Communications Technology (NICT): “[Alert] A Key Cause Behind Recent Data Leaks: Server Attacks Originating from App Analysis” (Published October 2026) https://www.nict.go.jp/press/2026/10/13-1.html
[Key Features of “THREAT-AQ”]
THREAT-AQ is a managed service that continuously monitors and visualizes externally observable security risks—such as vulnerabilities and misconfigurations in public web assets—prioritizing them to facilitate highly effective security countermeasures.
Continuous ASM Operations (External Asset Monitoring)
Continuously monitors public-facing client IT assets to visualize security risks like vulnerabilities and misconfigurations. Leveraging operational expertise built over nearly four years within the SHIFT Group, dedicated analysts evaluate risks, assign response priorities, and provide recommended countermeasures.
Three Specialized Monitoring Options for Comprehensive Threat Coverage
Beyond standard Web asset management, THREAT-AQ offers three optional monitoring add-ons to safeguard organizations against multi-dimensional risks:
■Credential Leak Monitoring
Continuously monitors the dark web and open internet for compromised email addresses, passwords, and credentials associated with company domains. Security analysts evaluate the impact and scope of detected leaks and provide recommendations to prevent unauthorized account access.
■Spoofing Monitoring
Monitors the internet for phishing sites (fake websites), lookalike domains, and counterfeit social media accounts targeting corporate names, domains, and brand/product names. Analysts investigate detected threats, assess potential brand damage, and deliver findings with recommended mitigation steps to protect customers and employees.
■Source Code Leak Monitoring
Scans public code repositories (such as GitHub) for leaks of proprietary source code or development credentials based on company domains and identifiers. When potential leaks are found, analysts analyze the exposure scope, assess intellectual property and intrusion risks, and guide appropriate response measures.
[Pricing]
Standard Service
Initial Fee: JPY 1,500,000 (tax excluded)
Monthly Fee: JPY 1,500,000 (tax excluded)
Optional Modules
Credential Leak Monitoring, Spoofing Monitoring, Source Code Leak Monitoring: Custom quotation
*Monthly fees vary depending on factors such as the number of monitored domains, alert frequency, report granularity, and emergency response scope.
*Minimum contract period is 12 months.
Service Page: https://contents.shiftinc.jp/threat-aq/
Inquiries: https://contents.shiftinc.jp/threat-aq/contact/
[SECURE AQ Service Lineup]
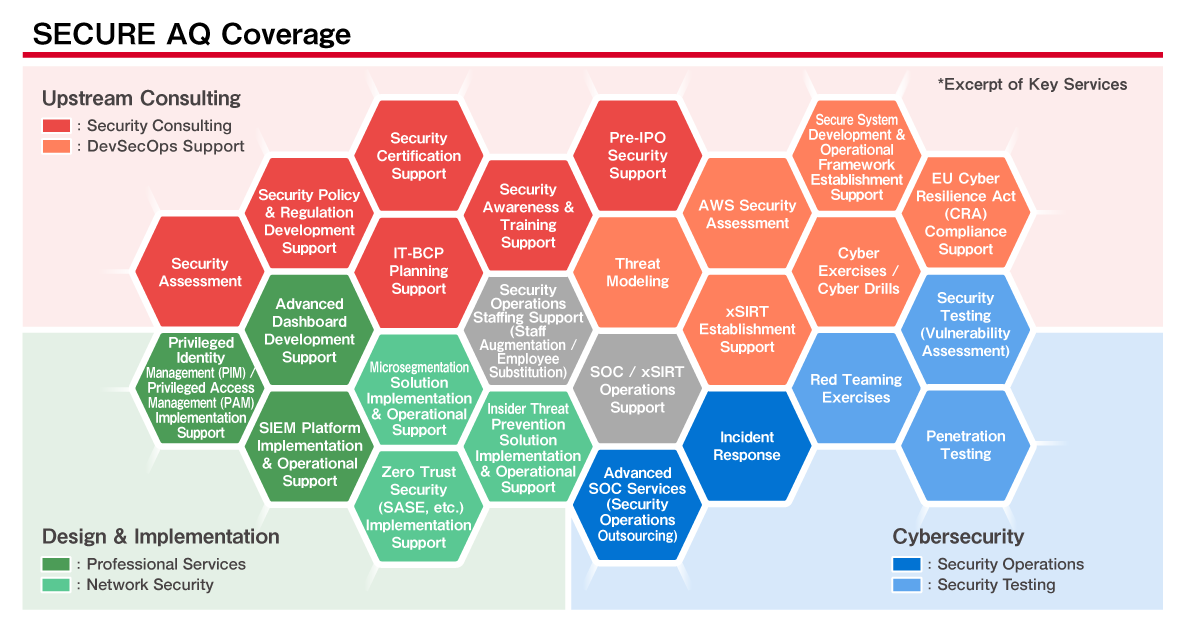
“SECURE AQ” offers optimal approaches tailored to customer phases and operational challenges, ranging from AI-powered automation of diagnostics, primary response, and routine operations, to specialized high-level professional support for complex issues difficult to solve with AI alone. From strategy formulation and framework construction to routine tool operations and ongoing adoption support, services will be offered across the following three areas based on client needs:
Upstream Consulting
Provides high-level professional support in strategy formulation and framework construction to address complex challenges difficult for AI alone to solve. From “Red Team Exercises” simulating real-world attacks to 24/7/365 SOC construction and CSIRT/PSIRT readiness consulting, SHIFT powerfully supports the reinforcement of enterprise-wide defense capabilities.
Design & Architecture
Beyond professional services such as privileged access management (PAM) setup and operation support, SIEM setup and operation support, and advanced dashboard development, SHIFT supports building secure environments tailored to client conditions, including network security such as network construction support and SASE/SSE architecture setup and operation.
Operations
Utilizing a network of over 250 auditors developed through proprietary training systems alongside industry-leading generative AI-driven vulnerability diagnostics, SHIFT accurately visualizes and manages latent risks across web applications, networks, and cloud environments. In addition, SHIFT provides comprehensive, hands-on support—from 24/7/365 SOC operations and primary incident response to tool adoption and routine log analysis. Going forward, SHIFT will drive further automation and operational efficiency by leveraging the expertise of its AI testing solution, “NEMURANAI.”
Special Webpage: https://service.shiftinc.jp/service_cat/security/
Service Inquiries: https://service.shiftinc.jp/contact/